Muhammad Aamir
Technology Risk & Digital Transformation Leader helping organisations govern, secure and modernise their technology.
Senior Manager, IT Risk Assurance · Co-founder, CertPrepX · Author · Educator
Technology Risk & Digital Transformation Leader helping organisations govern, secure and modernise their technology.
Senior Manager, IT Risk Assurance · Co-founder, CertPrepX · Author · Educator
 About
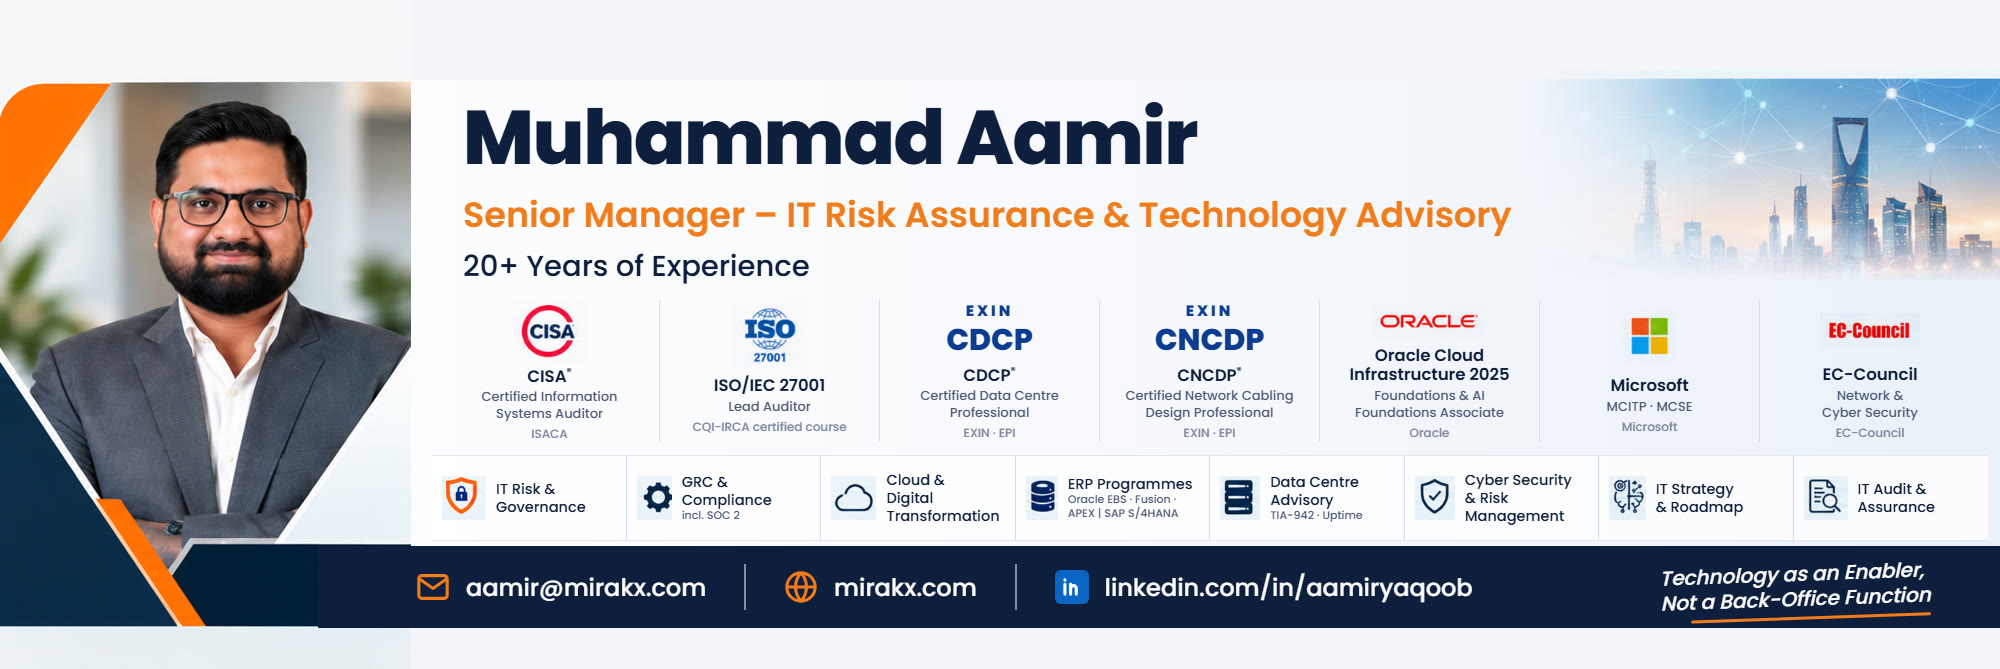
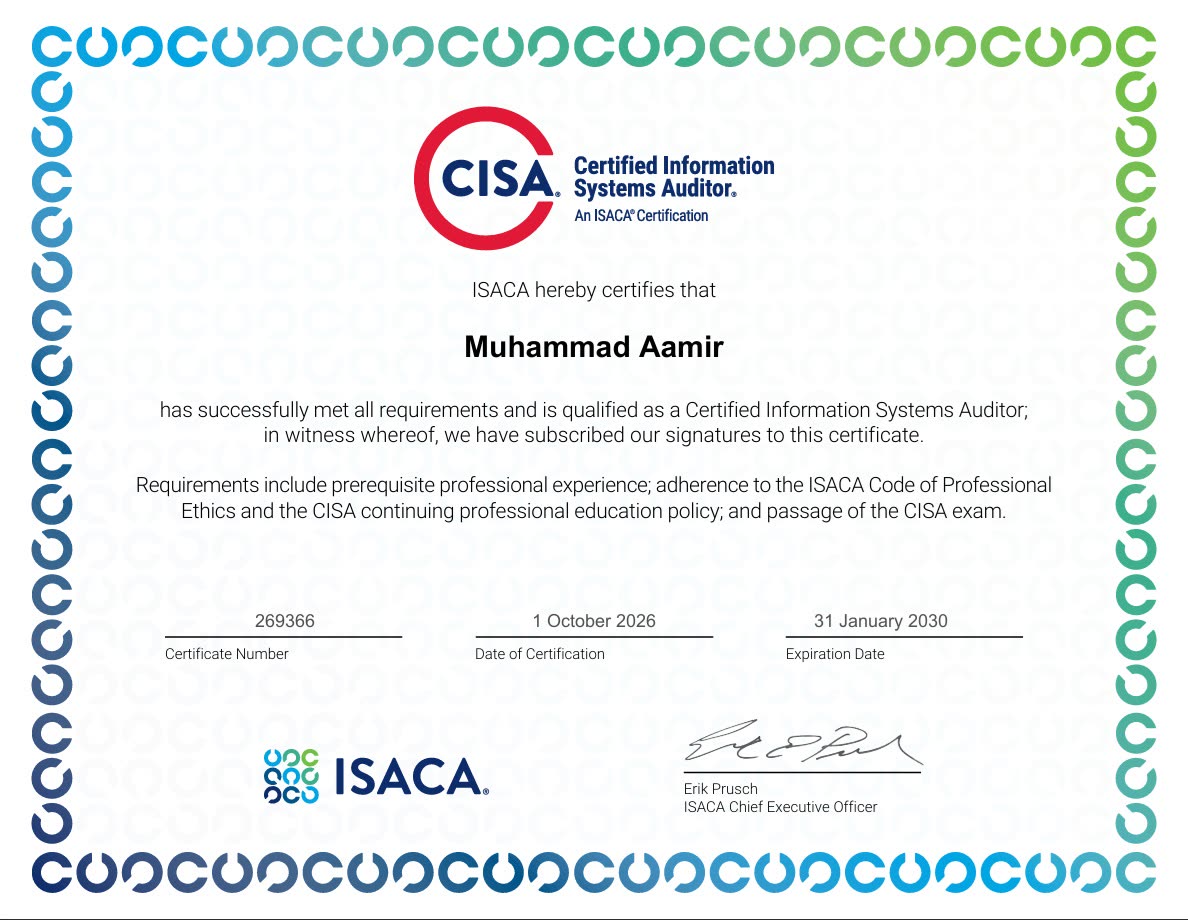
I am a Certified Information Systems Auditor (CISA) and Senior Manager in IT Risk Assurance & Technology Advisory, with over twenty years of experience leading IT audits, technology risk, ERP modernisation, automation and data integration across financial services, energy, healthcare, manufacturing, telecommunications and the public sector.
I advise senior executives on digital transformation, cloud adoption, data strategy and GRC, aligning technology investment with business strategy, governance and regulatory requirements.
I teach Data Systems Risks to Chartered Accountancy students, co-founded CertPrepX for certification candidates, and publish free explainers on technology, risk and AI.
Advisory, training and coaching grounded in real programme experience.
IT strategy and roadmaps, ERP and cloud programmes, technology selection and programme assurance.
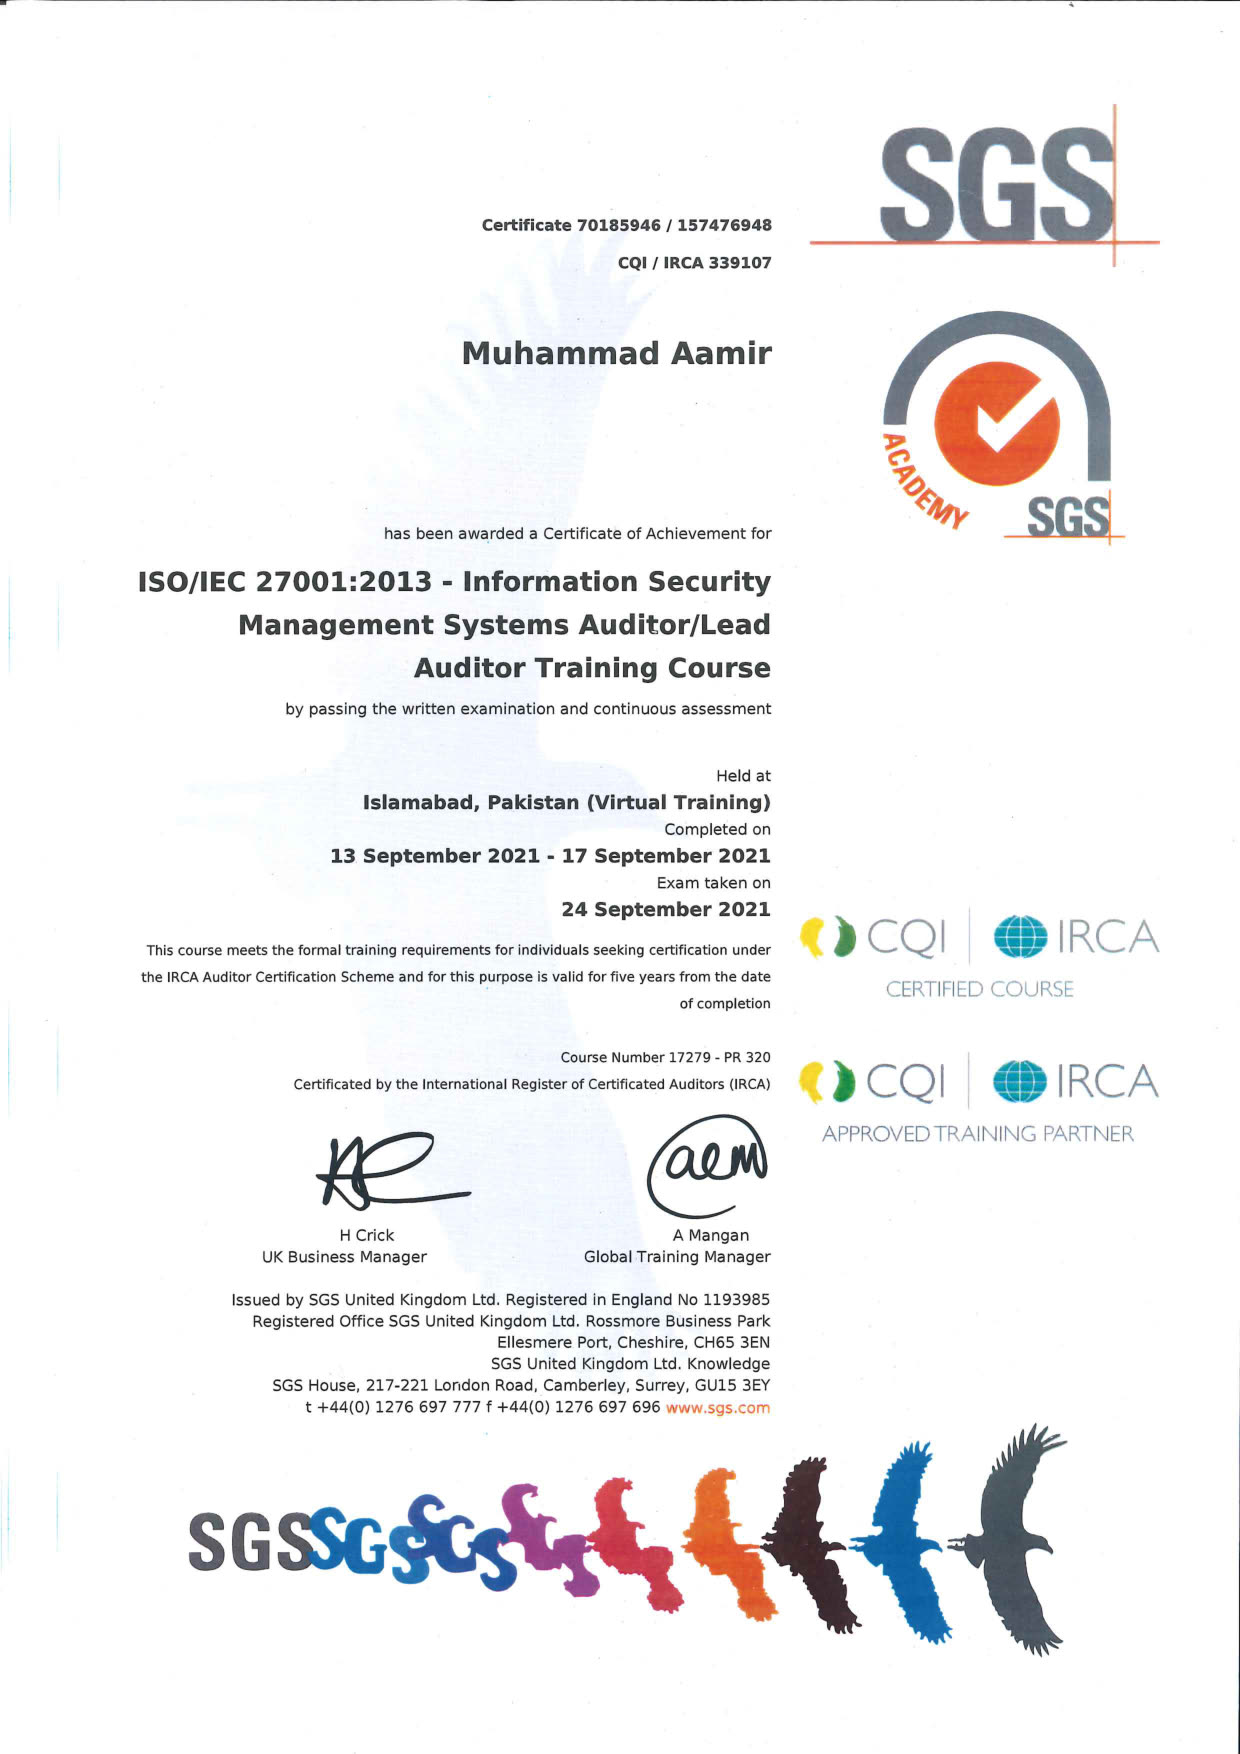
IT audits, ISO 27001 readiness, GRC frameworks and cyber security assessments.
Workshops on IT governance, cyber awareness, responsible AI and digital transformation.
CISA and ICAP CAF-3 Data, Systems & Risks preparation, from concepts to exam technique.
Exam-preparation platform for CISA, AAIA and ISO 27001 Lead Auditor candidates: realistic practice questions, mock exams, analytics and an adaptive study engine that shows exactly when you're ready to pass.
Hands-on depth across the full technology and risk landscape.
Enterprise transformation strategy, legacy modernisation, cloud migration, automation and business process re-engineering.
Technical Director on Oracle EBS, Oracle Fusion, Oracle APEX, SAP S/4HANA and Temenos T24 programmes, including the first Exadata/Exalogic implementation in Pakistan's banking sector.
IT audits, VAPT engagements and compromise assessments for banks, telecoms, energy companies and government bodies, aligned with COBIT, ISO 27001 and SBP requirements.
Defence-in-depth architectures, ISO 27001/22301 policy frameworks and readiness for GDPR, PCI-DSS and SBP mandates.
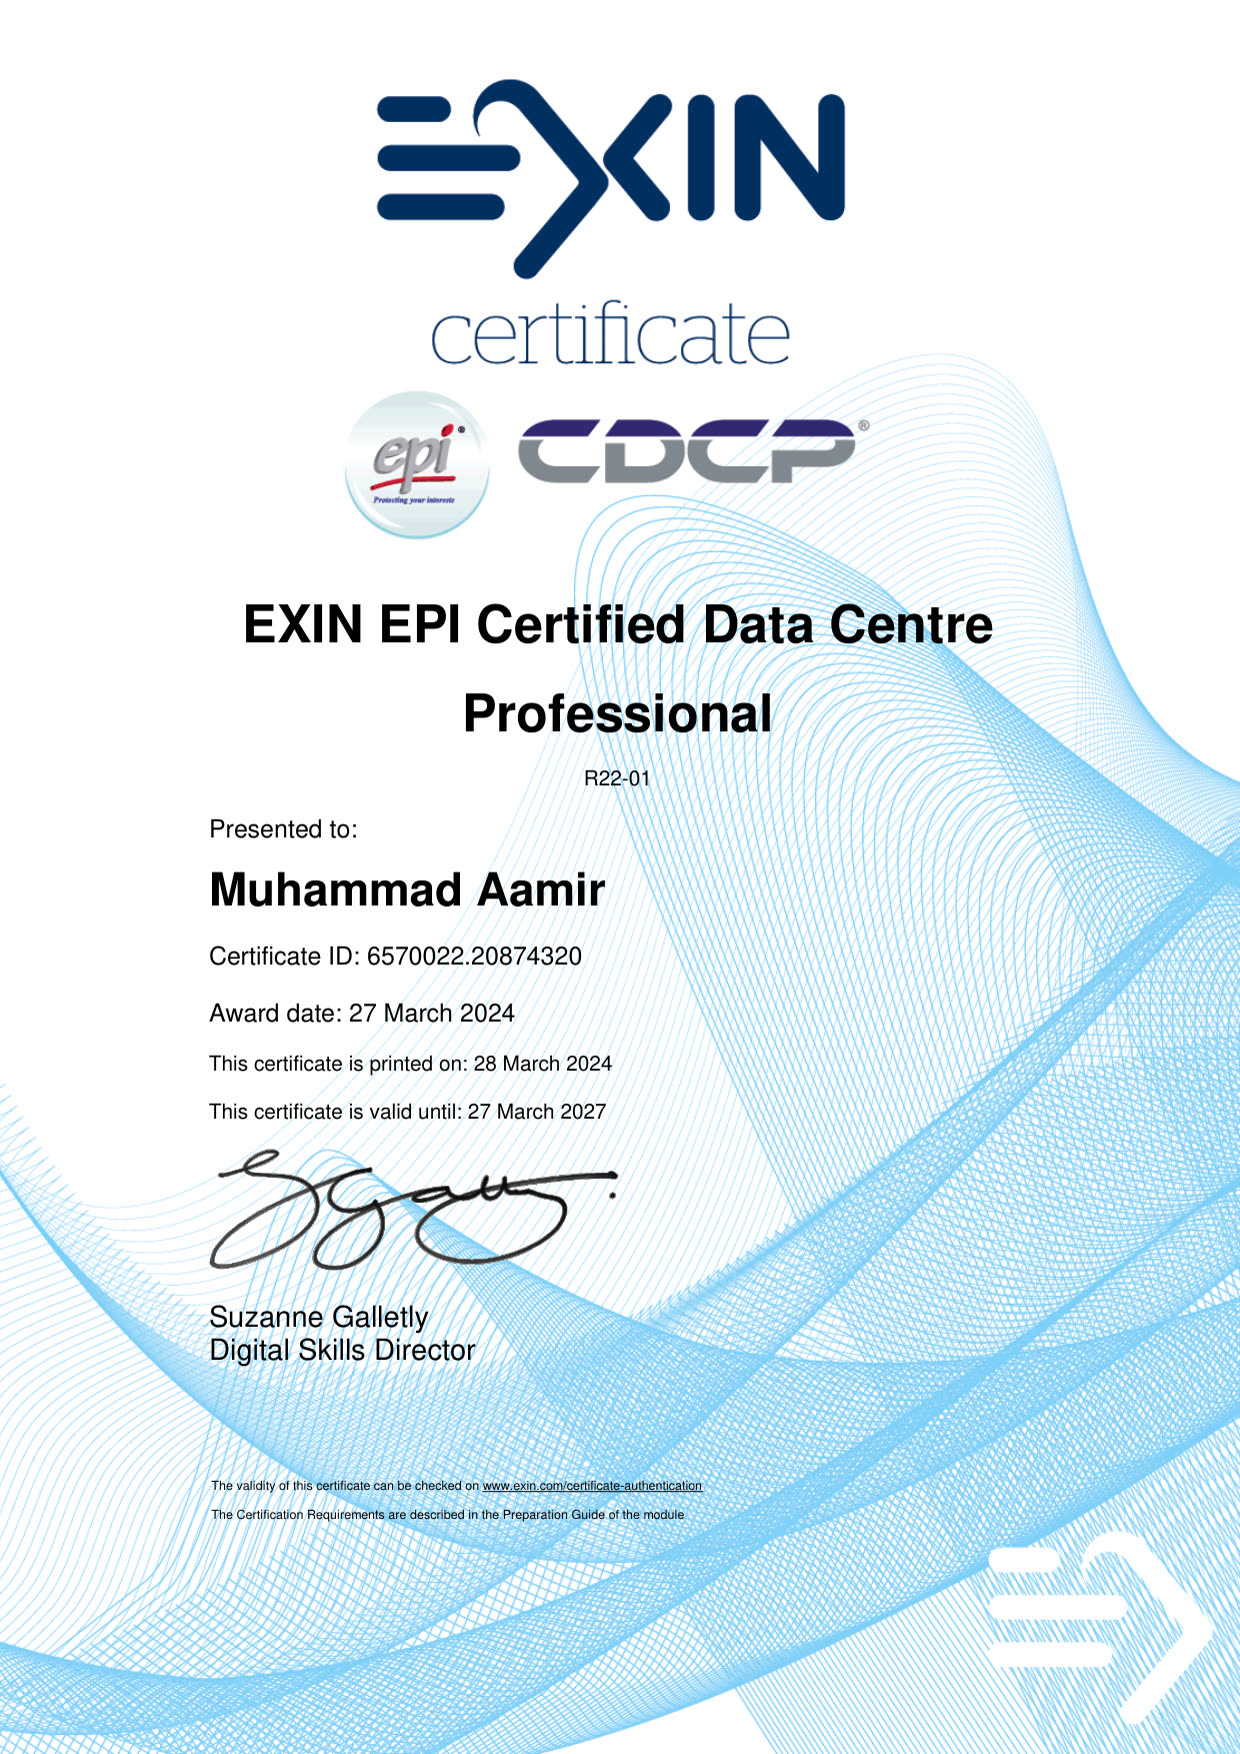
Lead consultant for TIA-942 Tier III data centres; enterprise platform sizing for high availability, disaster recovery and data loss prevention.
Governance for large programmes, including procurement of ~USD 35M under World Bank and PPRA rules and lifecycle cost analysis for ~USD 44M.
Selected transformation programmes across energy, healthcare, manufacturing and banking.
Study guides written for learners from non-IT backgrounds: plain language first, technical terms second.
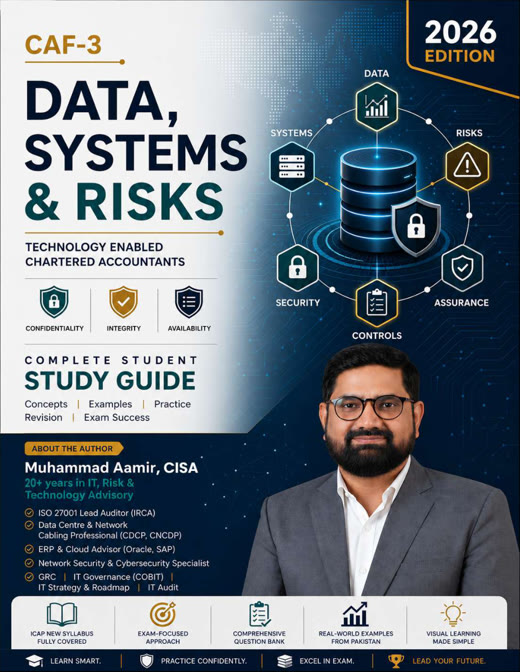
by Muhammad Aamir, CISA · 2026 Edition
All 17 chapters of the ICAP CAF-3 syllabus in plain language, with Pakistani examples, exam tips, sticky-note revision and hundreds of practice questions.
Download PDFAll five CISA domains condensed: key definitions, exam traps and decision rules for fast revision.
Practise on CertPrepXPlain-language explainers on cyber security, AI, IT audit and CISA preparation.
Practical guides on technology, risk and certification, written for non-technical readers.
The difference between hot, warm and cold recovery sites for the CISA exam, how RTO decides the choice, a practice question and the classic exam trap.
17 October 2026What a VPN really does on public Wi-Fi, explained with a simple postcard analogy, plus what a VPN can NOT protect you from.
Two decades of practical experience, passed on to the next generation.
Visiting Lecturer, Data Systems Risks, Islamabad.
Visiting Faculty (2013 – 2016): Software Engineering, Computer Architecture, System Programming and OOP.
Short explainers on AI, cyber security, IT audit and CISA preparation. Watch on YouTube →
MS Computer Science, The University of Lahore · Master of Computer Science, NUML Islamabad · BSc, University of Karachi
For advisory, training, speaking, coaching or book enquiries, I'd be glad to hear from you.